Rating
Innovation
Pricing
Technology
Usability
We have discovered similar tools to what you are looking for. Check out our suggestions for similar AI tools.
GitHub confirms 3,800 internal repos stolen through poisoned VS Code extension as supply chain worm hits Microsoft’s Python SDK
GitHub confirmed on May 20 that a poisoned VS Code extension installed on an employee’s device gave attackers access to roughly 3,800 internal repositories at the Microsoft-owned code storage and au [...]
Vercel breach exposes the OAuth gap most security teams cannot detect, scope or contain
One employee at Vercel adopted an AI tool. One employee at that AI vendor got hit with an infostealer. That combination created a walk-in path to Vercel’s production environments through an OAuth gr [...]
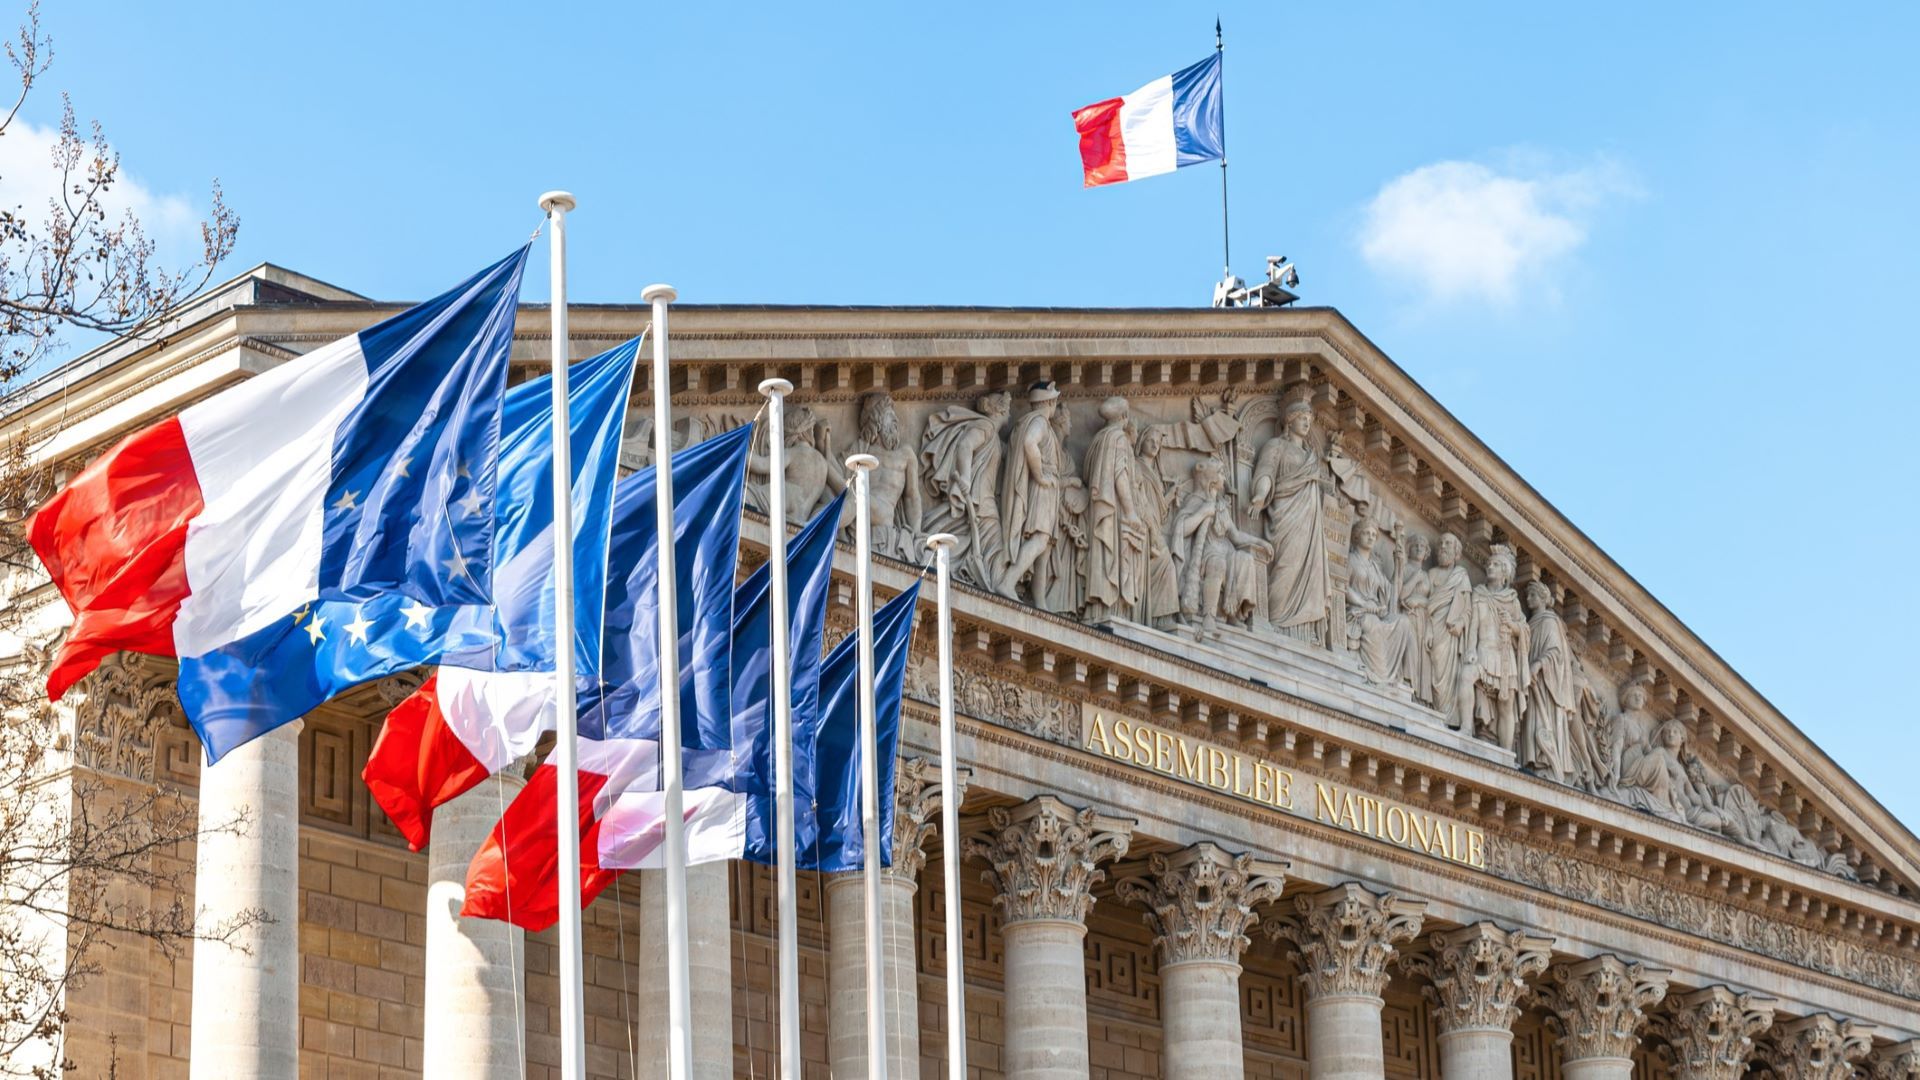
France’s ‘sovereign’ messenger Tchap was breached, and officials and the hacker disagree on how badly
France built its own encrypted messenger so civil servants would not have to trust WhatsApp or Telegram. Now that messenger has been breached, and the government and the attacker cannot agree on how m [...]
Protect your enterprise now from the Shai-Hulud worm and npm vulnerability in 6 actionable steps
Any development environment that installed or imported one of the 172 compromised npm or PyPI packages published since May 11 should be treated as potentially compromised. On affected developer workst [...]
Running Claude Code or Claude in Chrome? Here's the audit matrix for every blind spot your security stack misses
Between May 6 and 7, four security research teams published findings about Anthropic’s Claude that most outlets covered as three separate stories. One involved a water utility in Mexico, another tar [...]
Capital One releases VulnHunter, an open-source AI tool that finds software flaws before hackers do
Capital One on Thursday released VulnHunter, an open-source, agentic AI security tool that scans source code for exploitable vulnerabilities, maps out how an attacker would reach them, and proposes ta [...]
Four AI supply-chain attacks in 50 days exposed the release pipeline red teams aren't covering
Four supply-chain incidents hit OpenAI, Anthropic and Meta in 50 days: three adversary-driven attacks and one self-inflicted packaging failure. None targeted the model, and all four exposed the same g [...]